Security for the systems that run the plant.
ByteLock is an OT and ICS cybersecurity consultancy serving oil and gas, petrochemical and manufacturing asset owners. We assess, segment and harden industrial control networks, and ByteLock GRC maintains every risk, control and item of evidence in a single register.
Sector experience
Standards
Assessment and compliance services engineered for operations.
Every engagement is scoped around how the facility actually operates. We schedule activities around production, work alongside your control engineers and deliver prioritised, actionable findings.
OT risk assessment
Identify the cyber scenarios that could disrupt safety or production and quantify their likelihood and consequence. We model assets, zones and conduits, then rate each risk with your operations team in line with IEC 62443-3-2.
Vulnerability and gap assessment
Configuration-level review of Windows hosts, group policies, accounts, switches and firewalls against your target standard and CIS Benchmarks, performed passively so the process is never disturbed.
IEC 62443 compliance programs
Unified control registers that rationalise overlapping standards, with per-site compliance tracking and audit-ready evidence.
Architecture and segmentation
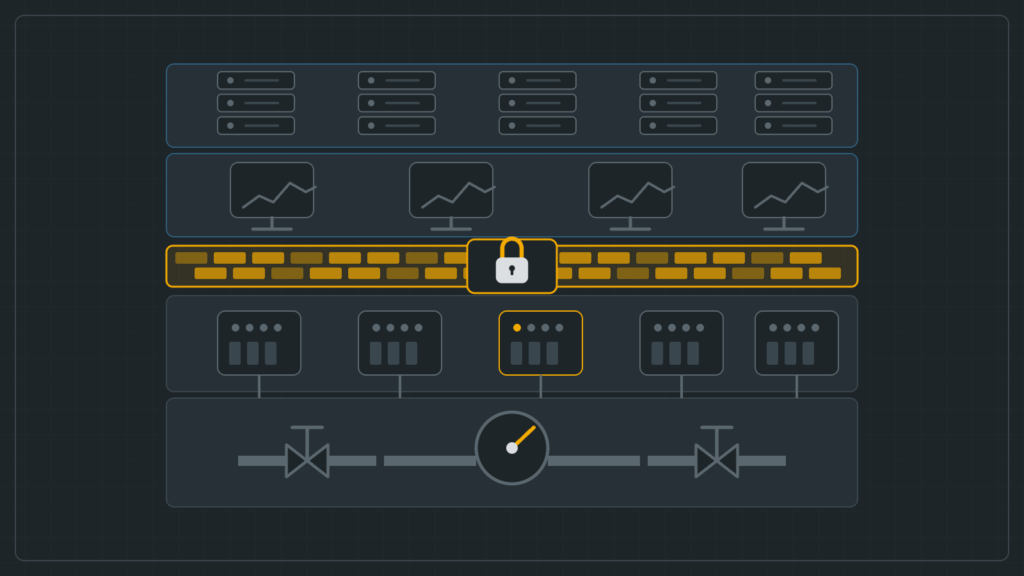
Zone and conduit design, OT reference architectures and industrial DMZ implementation aligned with IEC 62443-3-2, documented to switch-port level.
Backup and disaster recovery
Business impact analysis, recovery procedures and validated backups for servers, HMIs, PLCs and drives, supported by training for site personnel.
ISO/IEC 27001 internal audit
Stage 1 and Stage 2 internal audits, Statement of Applicability review and a compliance report prepared for your certification body.
Bars indicate the Purdue levels each service covers, from Level 0 at the base to Level 5 at the top. Amber denotes the industrial DMZ.
One register for every site, risk and control.
ByteLock GRC is a governance, risk and compliance platform purpose-built for OT. It is structured around the Purdue levels and asset classes your engineers already use, and maps every control to IEC 62443, NIST SP 800-82 and NERC CIP.
- Asset inventory
- Risk register
- Control library
- Incident log
- Remediation tracker
- Reports
| ID | Asset | Zone | Risk | Status |
|---|---|---|---|---|
| R-014 | Engineering workstation EWS-02 | Level 2 | High | Fix planned |
| R-009 | Historian to ERP link | DMZ | Medium | In progress |
| R-021 | PLC firmware, line 3 | Level 1 | Medium | Next shutdown |
| R-003 | Shared admin accounts | Level 3 | High | Closed |
| R-017 | Vendor remote access | DMZ | Low | Accepted |
Built from field work.
ByteLock applies hands-on field experience from refineries, oil fields and production facilities to every engagement, delivering assessments, audits and remediation across oil and gas, manufacturing and critical infrastructure.
Our services span risk, vulnerability and gap assessments aligned with ISA/IEC 62443, NIST, ISO/IEC 27001 and national regulatory frameworks, together with unified control registers, compliance tracking, OT reference architecture design, system hardening, penetration testing and backup and recovery validation.
About ByteLockView our services- Assess
- Risk, vulnerability and gap assessments of industrial control systems
- 62443
- Risk registers, zone and conduit design and compliance programs
- Field work
- Refineries, oil fields, petrochemical plants and production lines
- GRC
- ByteLock GRC maintains registers and remediation actions between audits
Insights
Perspectives on OT security, compliance and lessons from the field. Read all insights
- Write your incident response plan before you need it
 Decision authority, notification and when to isolate the plant: choices that should be made in advance, documented and rehearsed.
- The asset inventory: the control every other control depends onA device that is not known cannot be protected, patched or segmented. How to build an asset inventory and keep it current.
- Why OT security is not IT securityIndustrial control systems prioritise safety and availability, remain in service for decades and rely on protocols without authentication. OT security has to start there.
Tell us about your site.
Discuss an assessment, a compliance program, architecture work or a ByteLock GRC demonstration.