Insights
Perspectives on OT security, compliance and lessons from the field.

Write your incident response plan before you need it
Decision authority, notification and when to isolate the plant: choices that should be made in advance, documented and rehearsed.
The asset inventory: the control every other control depends on
A device that is not known cannot be protected, patched or segmented. How to build an asset inventory and keep it current.
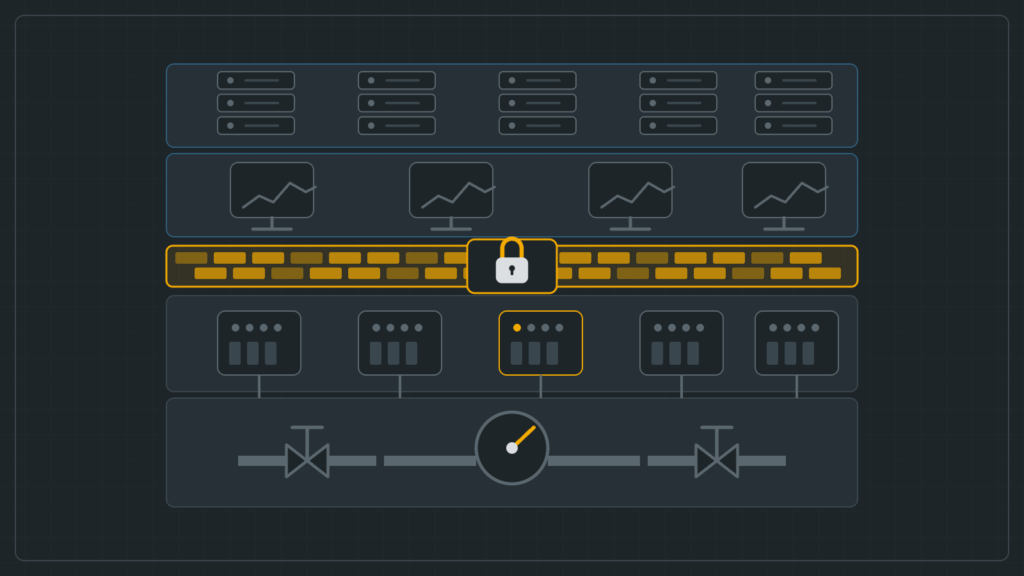
Why OT security is not IT security
Industrial control systems prioritise safety and availability, remain in service for decades and rely on protocols without authentication. OT security has to start there.
Compliance is not security, but it is a good place to start
Passing an audit confirms the right controls exist. How to close the gap between compliance and security, and make each reinforce the other.
Cyber risk is business risk: how to read a risk register
Express cyber risk in business terms, assign every risk an owner and a treatment decision, and the register becomes a tool leadership can act…
Why GRC matters: turning cybersecurity into a business discipline
Governance, risk and compliance answer the questions security tools cannot: who owns cyber risk, how much is acceptable and how assurance is demonstrated.